Is LinkedIn Scraping Legal? What LinkedIn's Own Lawsuits Show (2026)

Shehriar Awan●
17 Sept 2026

(updated)

●
13 min read

15-Second Summary

  1. Scraping LinkedIn is not a crime. US courts have said so, and nobody has ever been prosecuted for reading public pages
  2. It does break LinkedIn's User Agreement. That's a contract, not a law. The worst a normal user faces is a restricted account
  3. hiQ did not win. Eight months after the ruling everyone quotes, hiQ paid LinkedIn $500,000 and agreed to stop scraping forever
  4. Every scraper LinkedIn has sued did the same two things: fake accounts to get behind the login, and reselling the data
  5. GDPR applies even to public profiles. The CNIL fined Kaspr €240,000 for scraping LinkedIn contacts. It wants legitimate interest and an opt-out, not consent
  6. Sales Navigator is fine on your own paid seat. You're exporting what LinkedIn already shows you

So here you are... you googled "is LinkedIn scraping legal" and every article gives you the same answer. hiQ beat LinkedIn in 2022, scraping is legal, end of story.
15-Second Summary

That's half the story. And the wrong half.

Eight months after that ruling, hiQ agreed to pay LinkedIn $500,000 and never scrape again. Nobody mentions that part. So I read every lawsuit LinkedIn has filed against a scraper, the current User Agreement, the CNIL's decision and the new EDPB guidelines. Here's what they say.

Disclaimer

I'm not a lawyer. Everything below comes from primary sources I read myself: court opinions, regulator decisions and LinkedIn's own legal pages. It's context, not legal advice. Laws differ by country and change over time. If compliance matters to your business, talk to a qualified lawyer.

First things first. What does LinkedIn itself say?

Does LinkedIn allow data scraping?

No. And it's not subtle about it.

LinkedIn's User Agreement, effective 3 November 2025, has a section 8.2 called "Don'ts". Here's the one that matters:

Develop, support or use software, devices, scripts, robots or any other means or processes (such as crawlers, browser plugins and add-ons or any other technology) to scrape or copy the Services, including profiles and other data from the Services

Two more bullets matter later. Bullet 1 bans creating "a false identity on LinkedIn" or using "another's account". Bullet 11 bans renting, selling or otherwise monetising "the Services or related data" without LinkedIn's consent.
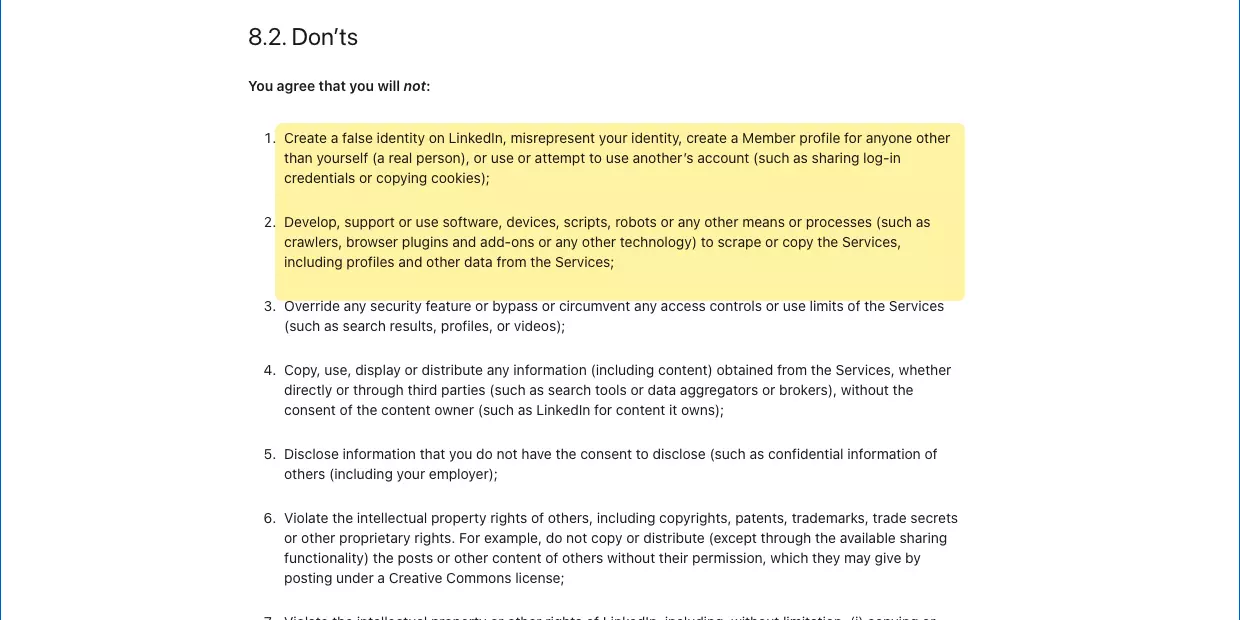
LinkedIn User Agreement section 8.2, with the false-identity and scraping bullets highlighted
Notice what's missing. No exception for public data, none for your own account. A Python script, a Chrome extension and a LinkedIn bot all fall under the same clause.
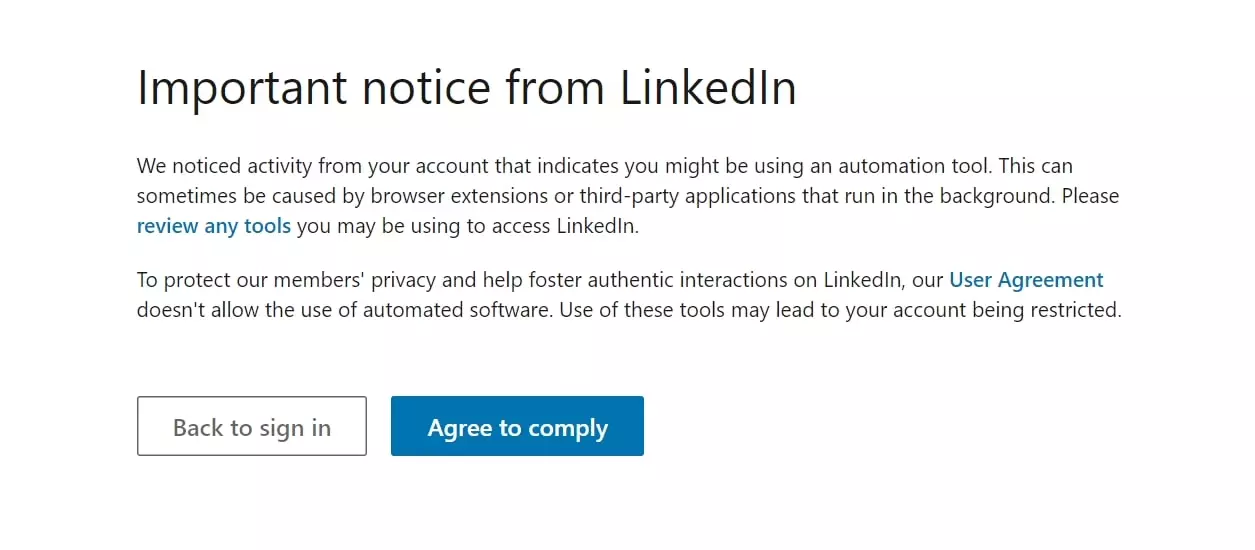
So what happens if LinkedIn catches you? Its help centre says your account gets restricted, then re-enabled once you disable the tool. This is the message people get:
LinkedIn notice warning that automation tools may lead to account restriction
"Then just use the official API", someone will say. Except the Profile API only returns data about the person who logged in. Nobody else. The paid side isn't better, see the Sales Navigator API article.

OK, so LinkedIn doesn't allow it. But does "against LinkedIn's rules" mean "illegal"?

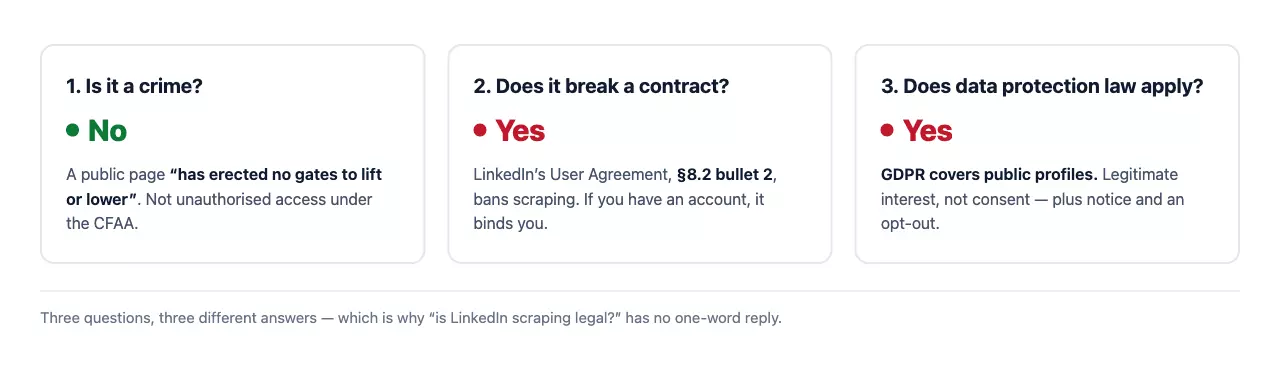
Let me break this down into three questions, because they have three different answers:

  1. Is it a crime?
  2. Does it break a contract?
  3. Does data protection law apply?
Three answers: not a crime, breaks the contract, GDPR still applies

Courts answered the first two in the case everyone quotes.

hiQ vs LinkedIn: the full story

In 2017, LinkedIn sent hiQ Labs a cease-and-desist letter for scraping public profiles. hiQ sued first.
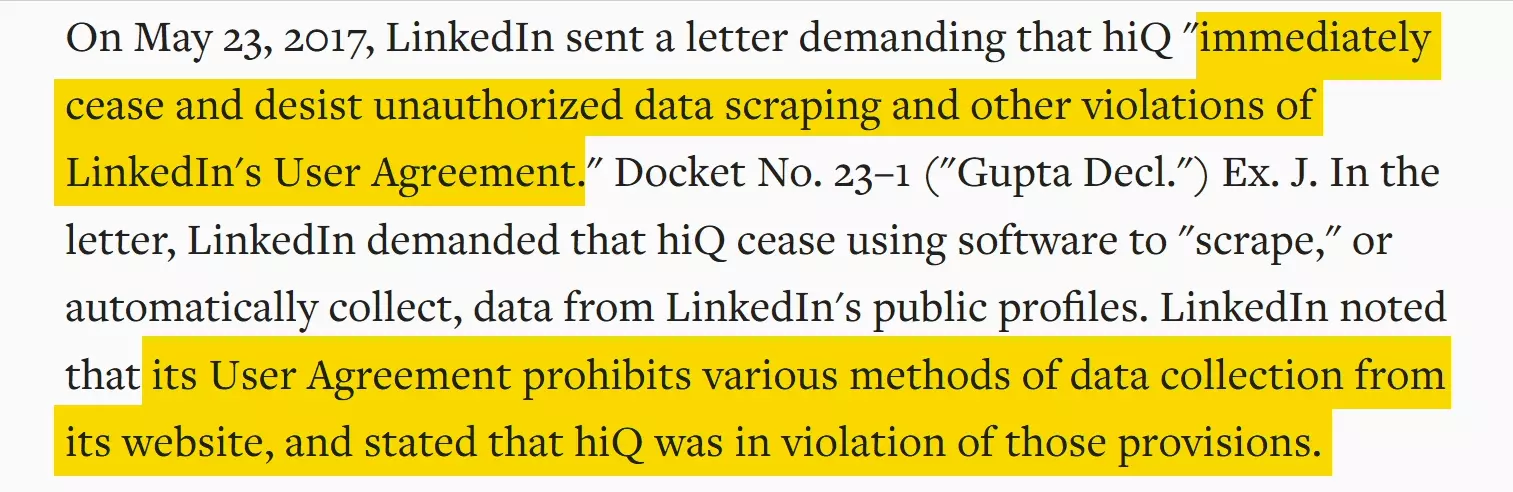
Excerpt of LinkedIn's 2017 cease-and-desist letter to hiQ Labs
In April 2022, the Ninth Circuit ruled in hiQ's favour on one point. Scraping a public page is probably not "access without authorization" under the CFAA, America's anti-hacking law. In the court's words, a public page "has erected no gates to lift or lower".

That's the headline that went around the world.
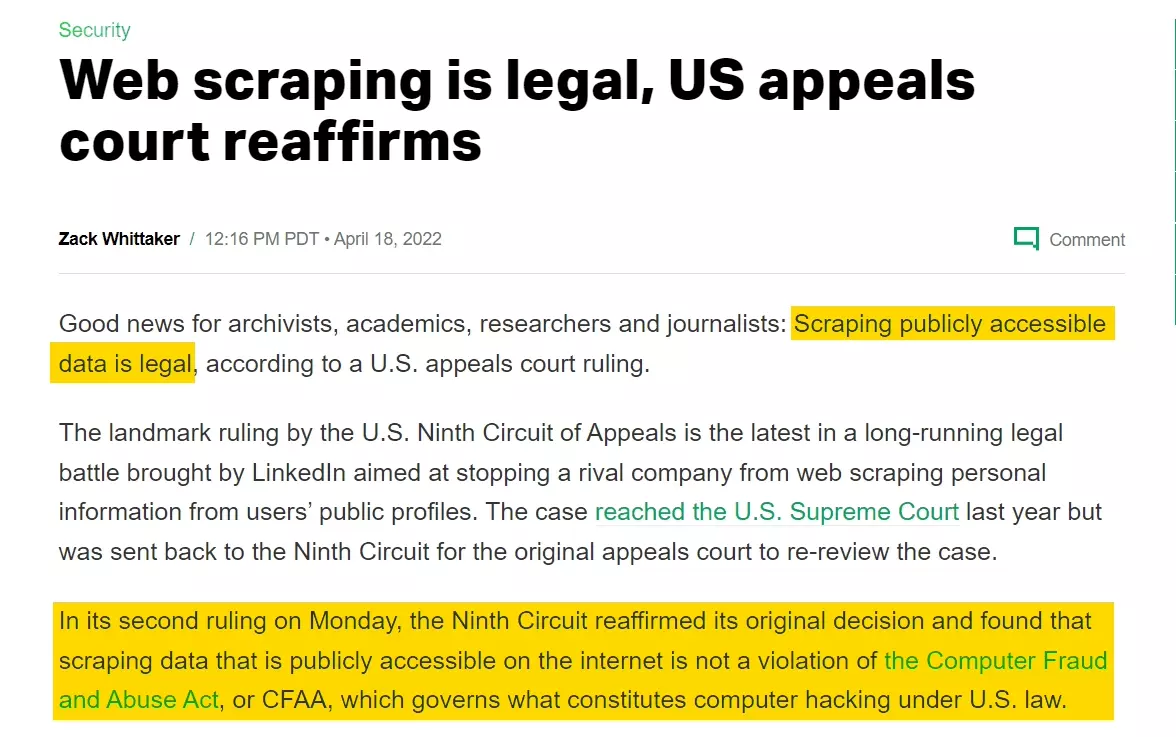
TechCrunch headline, April 2022: web scraping is legal

But read the actual ruling and it's much narrower. A preliminary decision, about one criminal law. The same judges listed everything LinkedIn could still sue over: breach of contract, trespass, misappropriation, unjust enrichment.
And LinkedIn did exactly that. On 4 November 2022, the district court ruled that hiQ had breached LinkedIn's User Agreement. hiQ had LinkedIn accounts, including fake ones created by its contractors, so the terms applied to it.
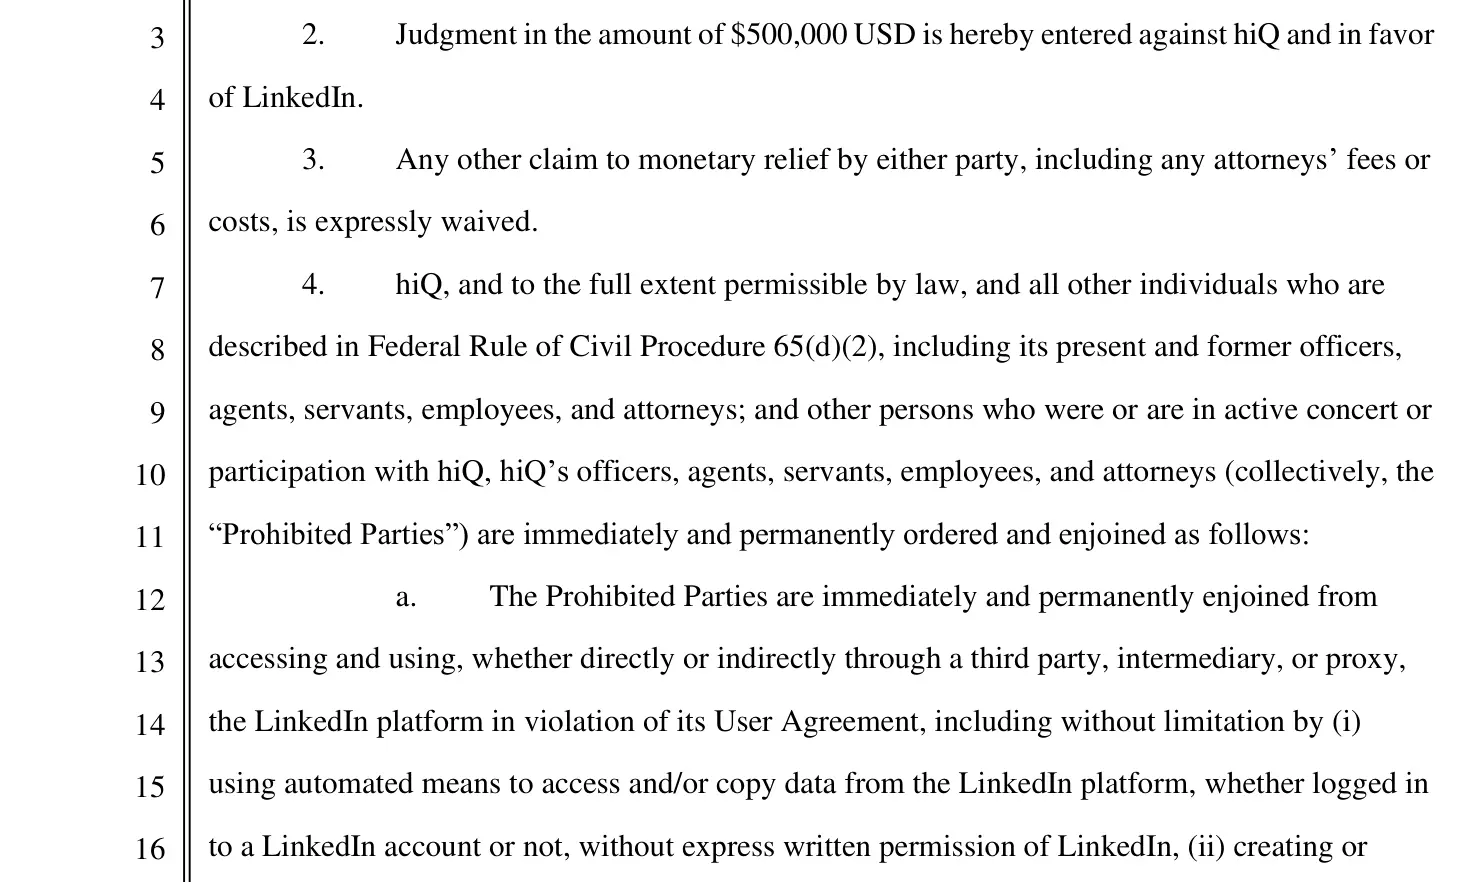
A month later, hiQ signed a consent judgment. It paid LinkedIn $500,000, accepted a permanent ban on scraping, and agreed to destroy everything it had collected. hiQ hasn't touched a LinkedIn profile since.
hiQ's consent judgment: $500,000 entered against hiQ, and a permanent injunction on scraping

So what did we learn from hiQ?

  1. Scraping public pages is not hacking βœ…
  2. Breaking LinkedIn's terms is not a crime βœ…
  3. But if you have a LinkedIn account, those terms are a contract, and LinkedIn can sue you over it ❌
The same logic applies to Google Maps. Now the three cases nobody talks about.

Mantheos, Proxycurl and ProAPIs: the pattern

LinkedIn has sued three more scrapers since hiQ. Every one did the same two things.
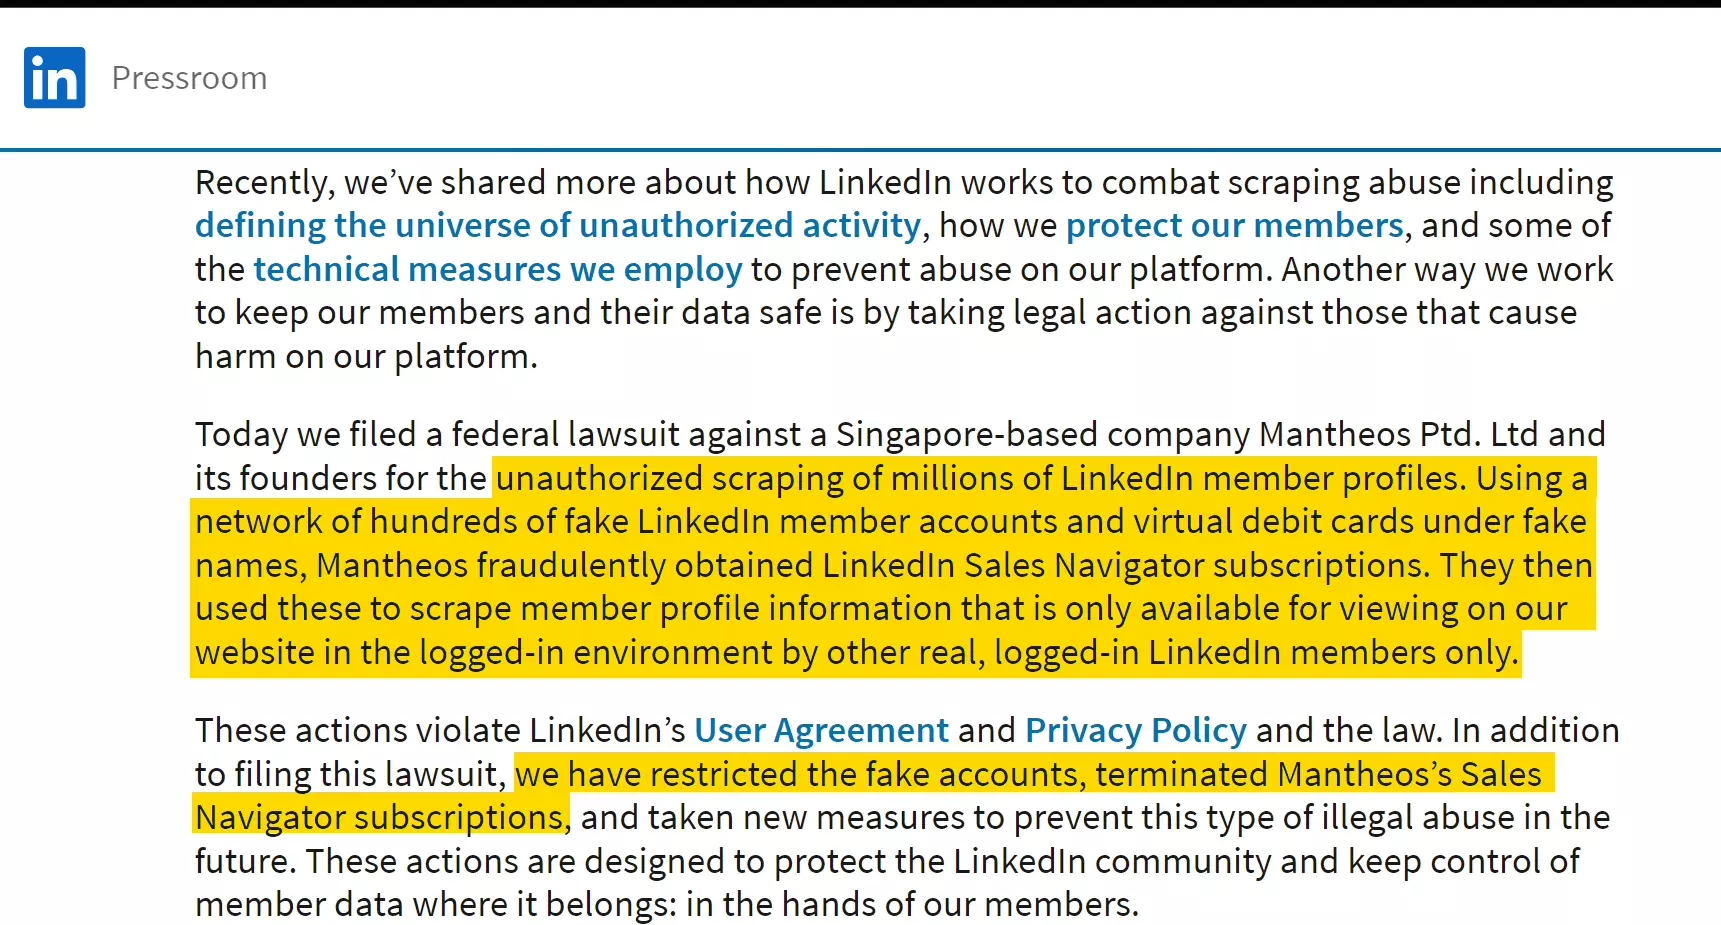
Mantheos (2022). A Singapore company used "hundreds of fake LinkedIn member accounts and virtual debit cards under fake names" to buy Sales Navigator seats and scrape behind the login. LinkedIn sued in February and settled in May. Data deleted, software destroyed.
LinkedIn pressroom statement on the Mantheos lawsuit, fake accounts highlighted
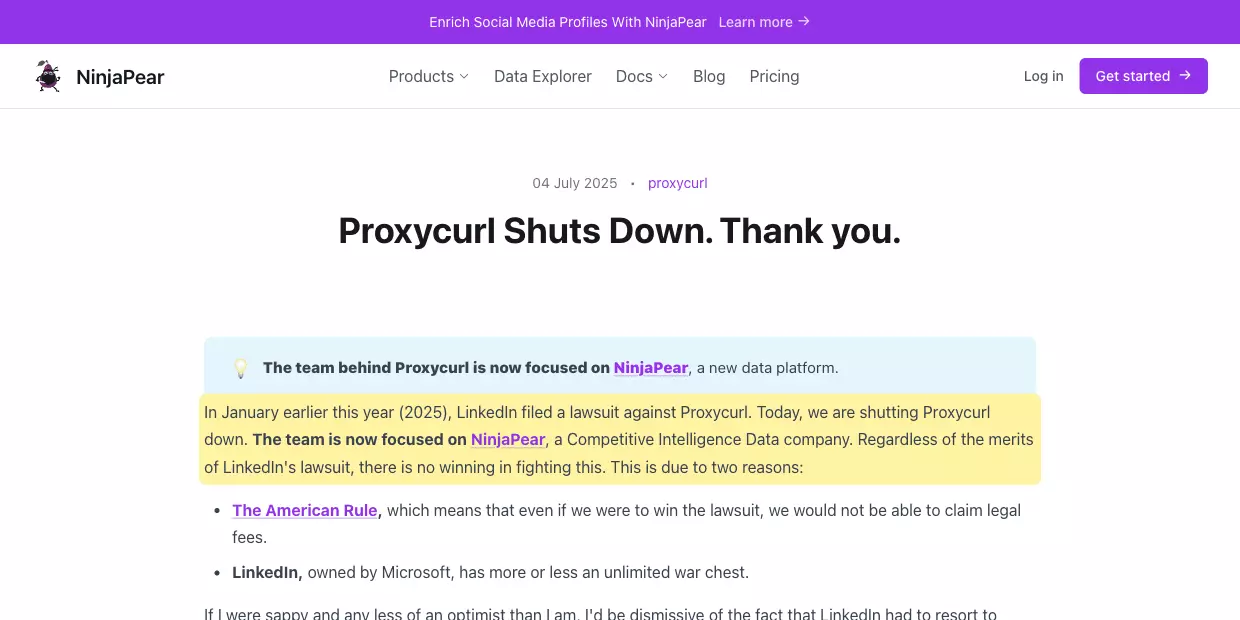
Proxycurl (2025). LinkedIn sued Nubela, the company behind the Proxycurl API, in January 2025. Same story: fake accounts, plus a profile database sold to customers. LinkedIn's announcement spells out the result: permanent injunction, all data deleted. Proxycurl shut down in July 2025.
Proxycurl's shutdown post, 4 July 2025, citing LinkedIn's lawsuit
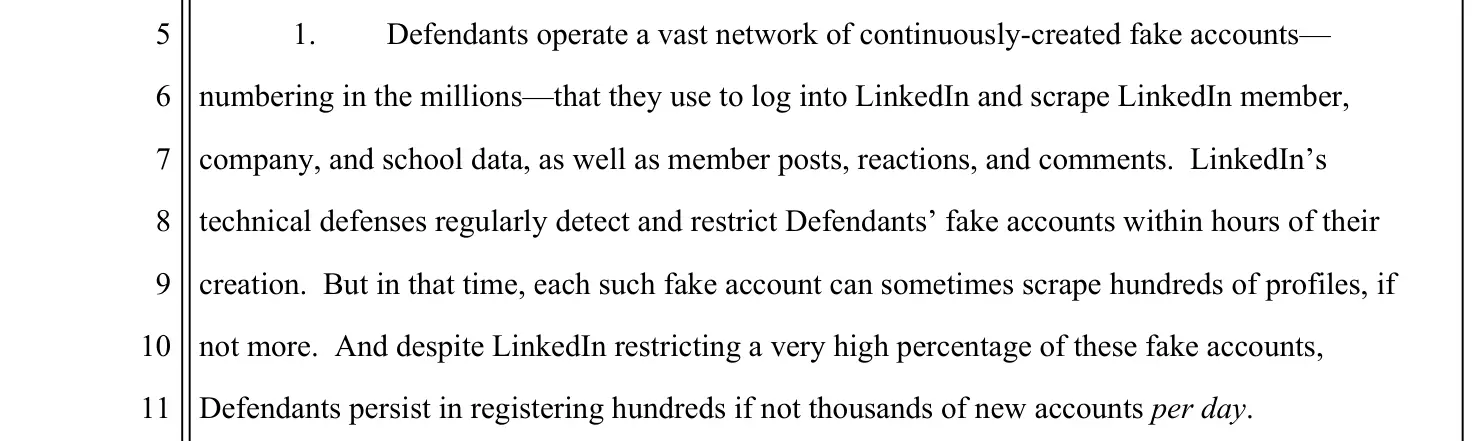
ProAPIs (2025 to 2026). LinkedIn filed case 5:25-cv-08393 in October 2025, against the company and its founder personally. The first paragraph of the complaint is about fake accounts behind the password wall. Both sides agreed to settle in February 2026.
LinkedIn v. ProAPIs complaint, paragraph 1, on a network of millions of fake accounts
See the pattern? LinkedIn doesn't even argue "scraping is hacking" any more. Every complaint starts with breach of contract and fraud, because every defendant used fake or bought accounts to build a database and sold it to people who never paid LinkedIn a cent.
Drake meme: no to creating fake accounts, yes to using your own account
One more case worth knowing. In Meta vs Bright Data, January 2024, Bright Data scraped Facebook while logged out, and the court said Meta's terms didn't apply to someone who never used the service. Log in, and that argument is gone.

So what does all this mean for a normal person with a normal account?

What you actually risk
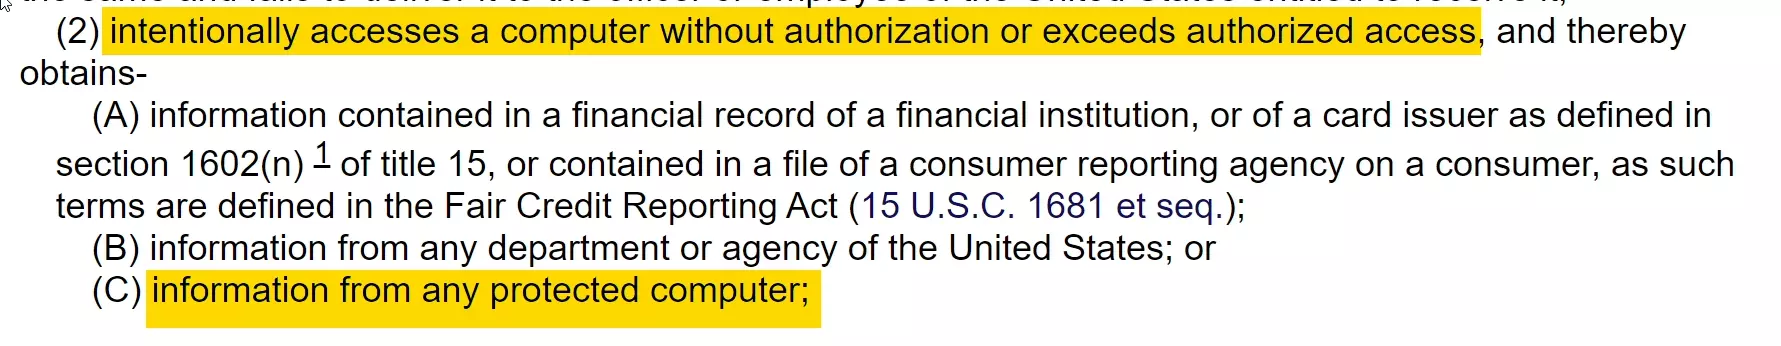
You're not going to prison. No US court has ever convicted anyone under the CFAA for reading public pages. In France, the criminal offence requires bypassing a security measure, and reading a page you were shown doesn't count.
Text of the Computer Fraud and Abuse Act, 18 U.S.C. 1030(a)(2)
You can lose your account. This is the real risk. LinkedIn spots automation by how you behave, not by counting to a magic number. Every limit it enforces is in LinkedIn limits, and how modern bot detection works explains what gets you flagged.

You won't get sued unless you earn it. Four defendants in nine years, all commercial operations running fake accounts and reselling data. If that's not your business model, you're not on LinkedIn's list.

One caveat. If LinkedIn sends you a cease-and-desist, blocks your IP and you keep going, that becomes a CFAA problem, per Facebook vs Power Ventures. If LinkedIn writes to you, stop.

That's the US side. But what about Europe, where the rules protect the people in the data, not the website?

Does GDPR apply to public LinkedIn profiles?
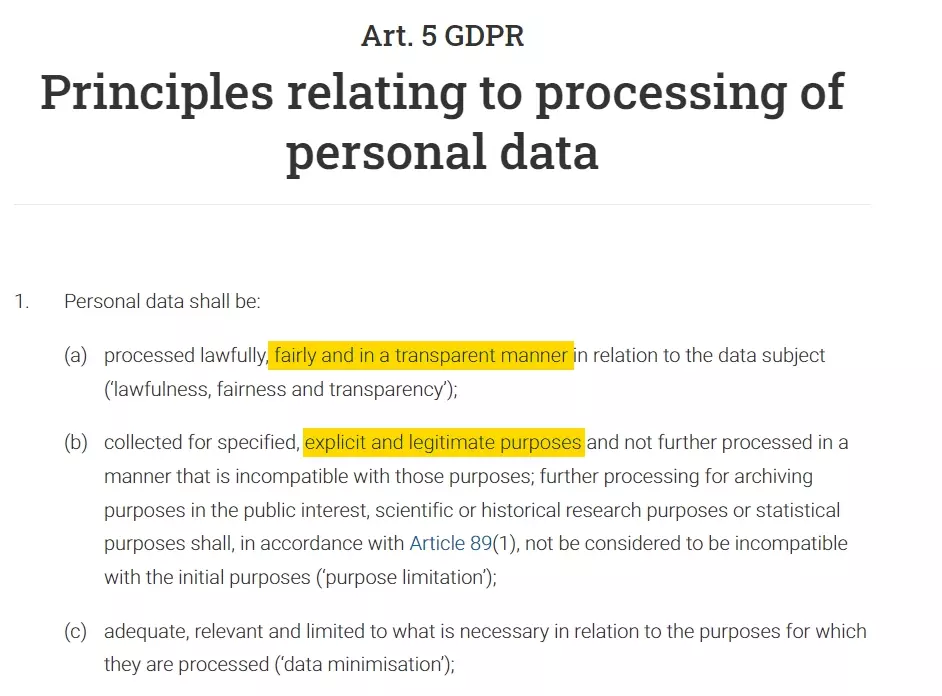
Yes. A name, a job title and an employer are personal data under Article 4, no matter who can see them. Making your profile public doesn't change that.
GDPR Article 5, principles relating to processing of personal data
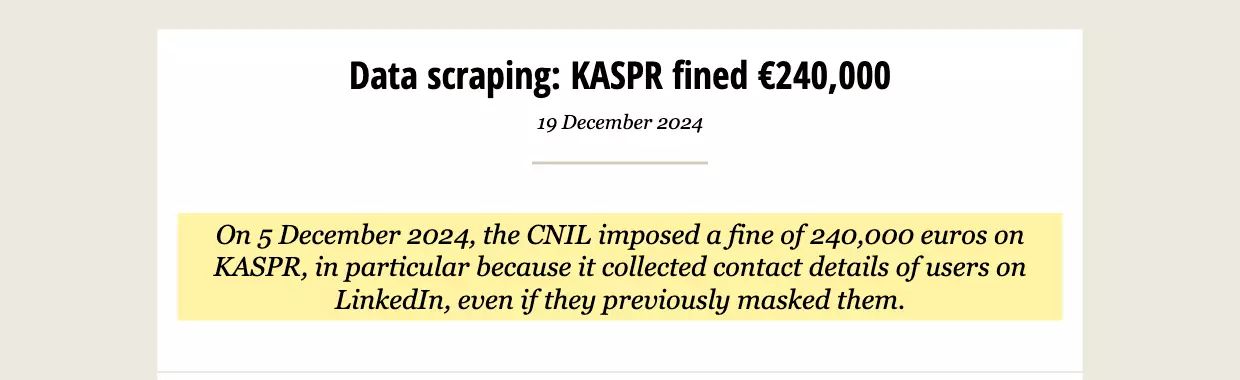
And there's proof. On 5 December 2024, the French regulator CNIL fined Kaspr €240,000. Kaspr sold a Chrome extension that pulled contact details from LinkedIn profiles into a B2B prospecting database.
CNIL fining Kaspr 240,000 euros for collecting LinkedIn contact details
What did Kaspr do wrong? The decision is clear. Kaspr collected contact details from people who had limited their visibility to first-degree connections. The CNIL said a member's visibility setting binds everyone, and hiding a field is a way of saying no.
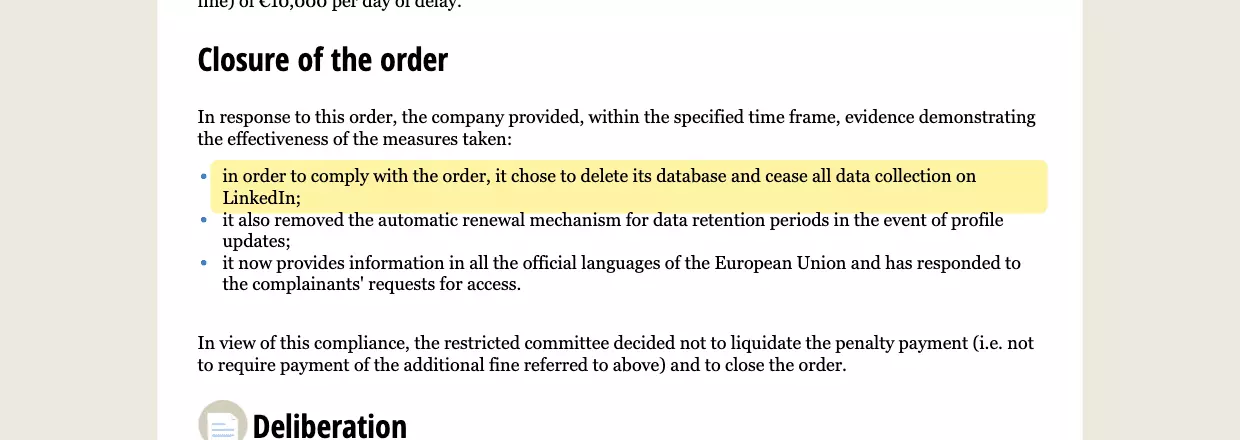
Kaspr also kept the data indefinitely and never told anyone. And the fine was the small part. In March 2026, the CNIL closed the case because Kaspr had deleted its 160 million contacts and stopped collecting from LinkedIn altogether.
CNIL closure notice: Kaspr deleted its database and stopped collecting on LinkedIn
So does GDPR ban LinkedIn scraping? No. And here's where most articles get it backwards: GDPR does not require consent to scrape. The basis regulators point to is legitimate interest, Article 6(1)(f). The CNIL's own focus sheet says B2B prospecting can rely on it.

But legitimate interest comes with homework:

  1. Tell people where you got their data (Article 14)
  2. Only collect what you need, and only keep it as long as you need it
  3. Give people an easy way to object, and respect it
  4. Leave alone anything the member hid or restricted
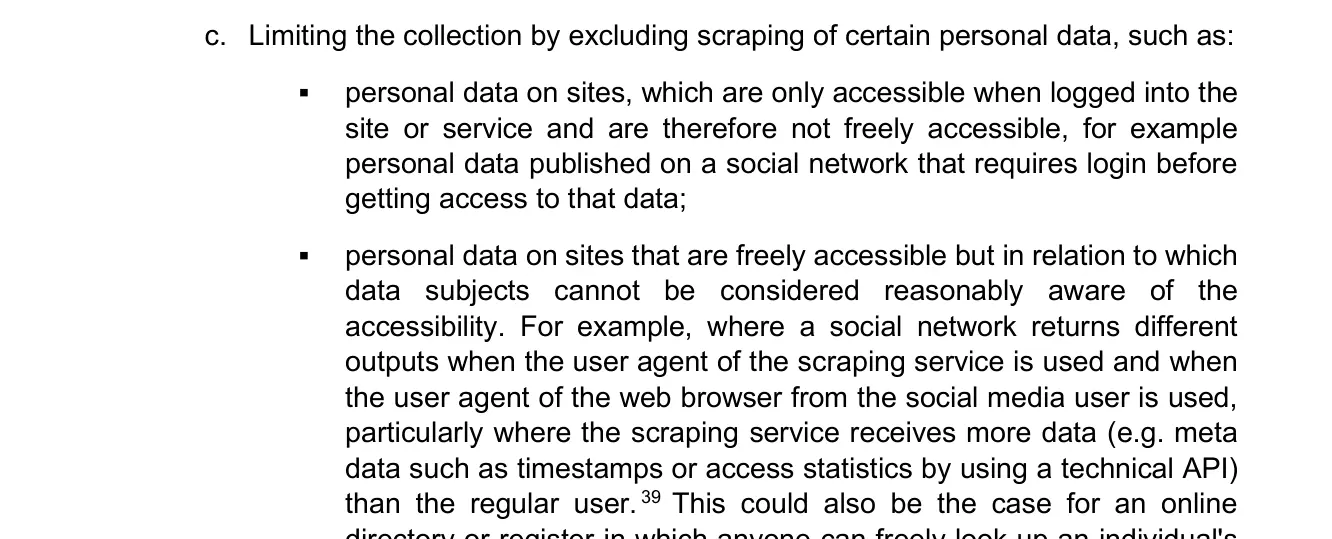
The EDPB, Europe's umbrella regulator, said the same in its Guidelines 03/2026 on web scraping, adopted in July 2026. Consent isn't the realistic basis, and data "only accessible when logged into the site" should be excluded.
EDPB Guidelines 03/2026, paragraph 66(c), excluding data behind a login

The guidelines target AI training, but every regulator in Europe will apply the same reading to any scraper.

Cold-emailing those contacts has its own rules, covered in extracting emails from LinkedIn.

Now, the question I get asked most. What about Sales Navigator, since it's behind a paywall?

People assume Sales Navigator is the risky end, because you pay to see it. Look at who actually got sued and it's the opposite.
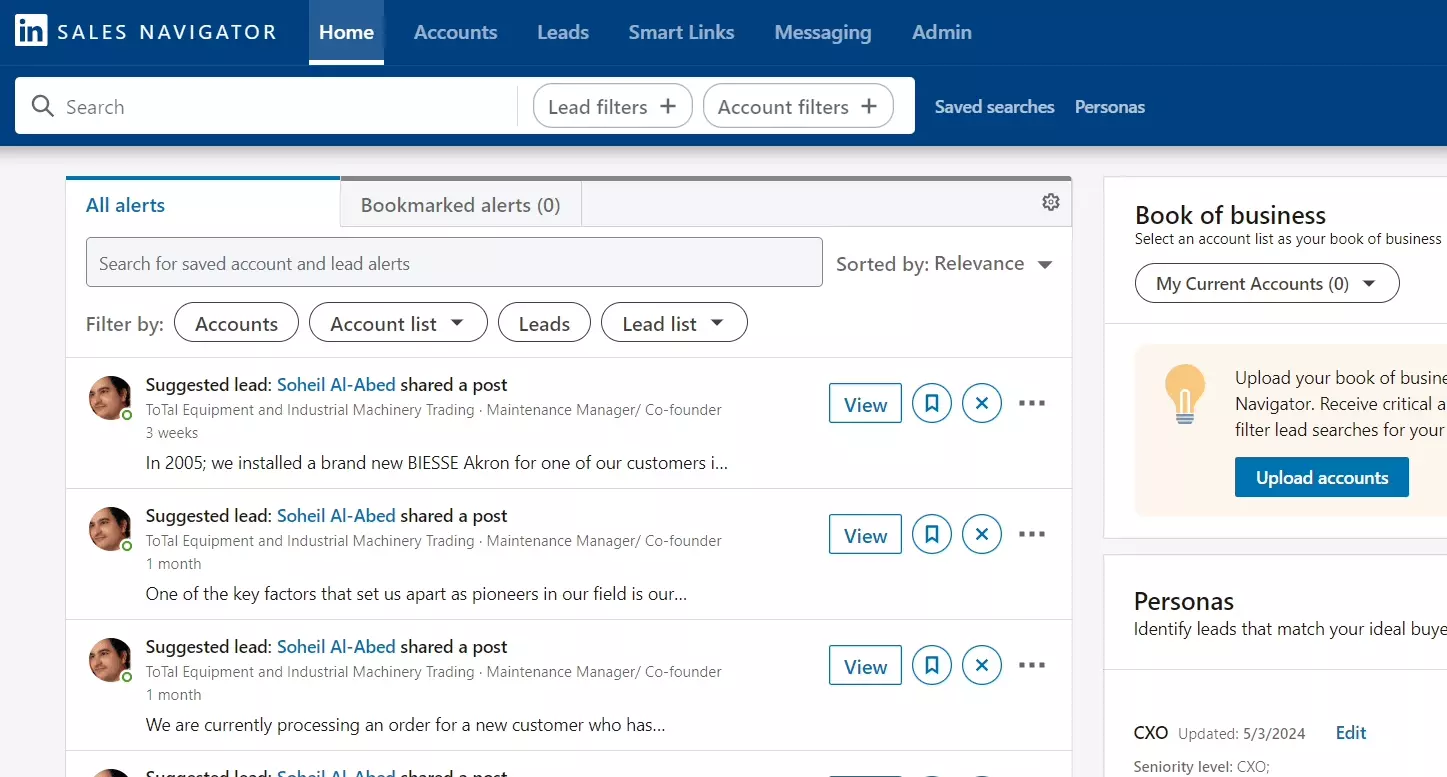
Sales Navigator home screen with lead alerts

Mantheos, Proxycurl and ProAPIs all got behind the paywall with fake accounts, paid for under fake names, to resell the data to people who never bought a subscription. That's fraud on top of a broken contract.

Now compare that to you. You pay LinkedIn for a Sales Navigator seat, log in with your own real profile, and export the leads already on your screen.

You have legitimate access, you're not giving anyone data they couldn't see themselves, and you didn't create a fake identity. Bullets 1 and 11, the two every defendant broke, don't apply to you.
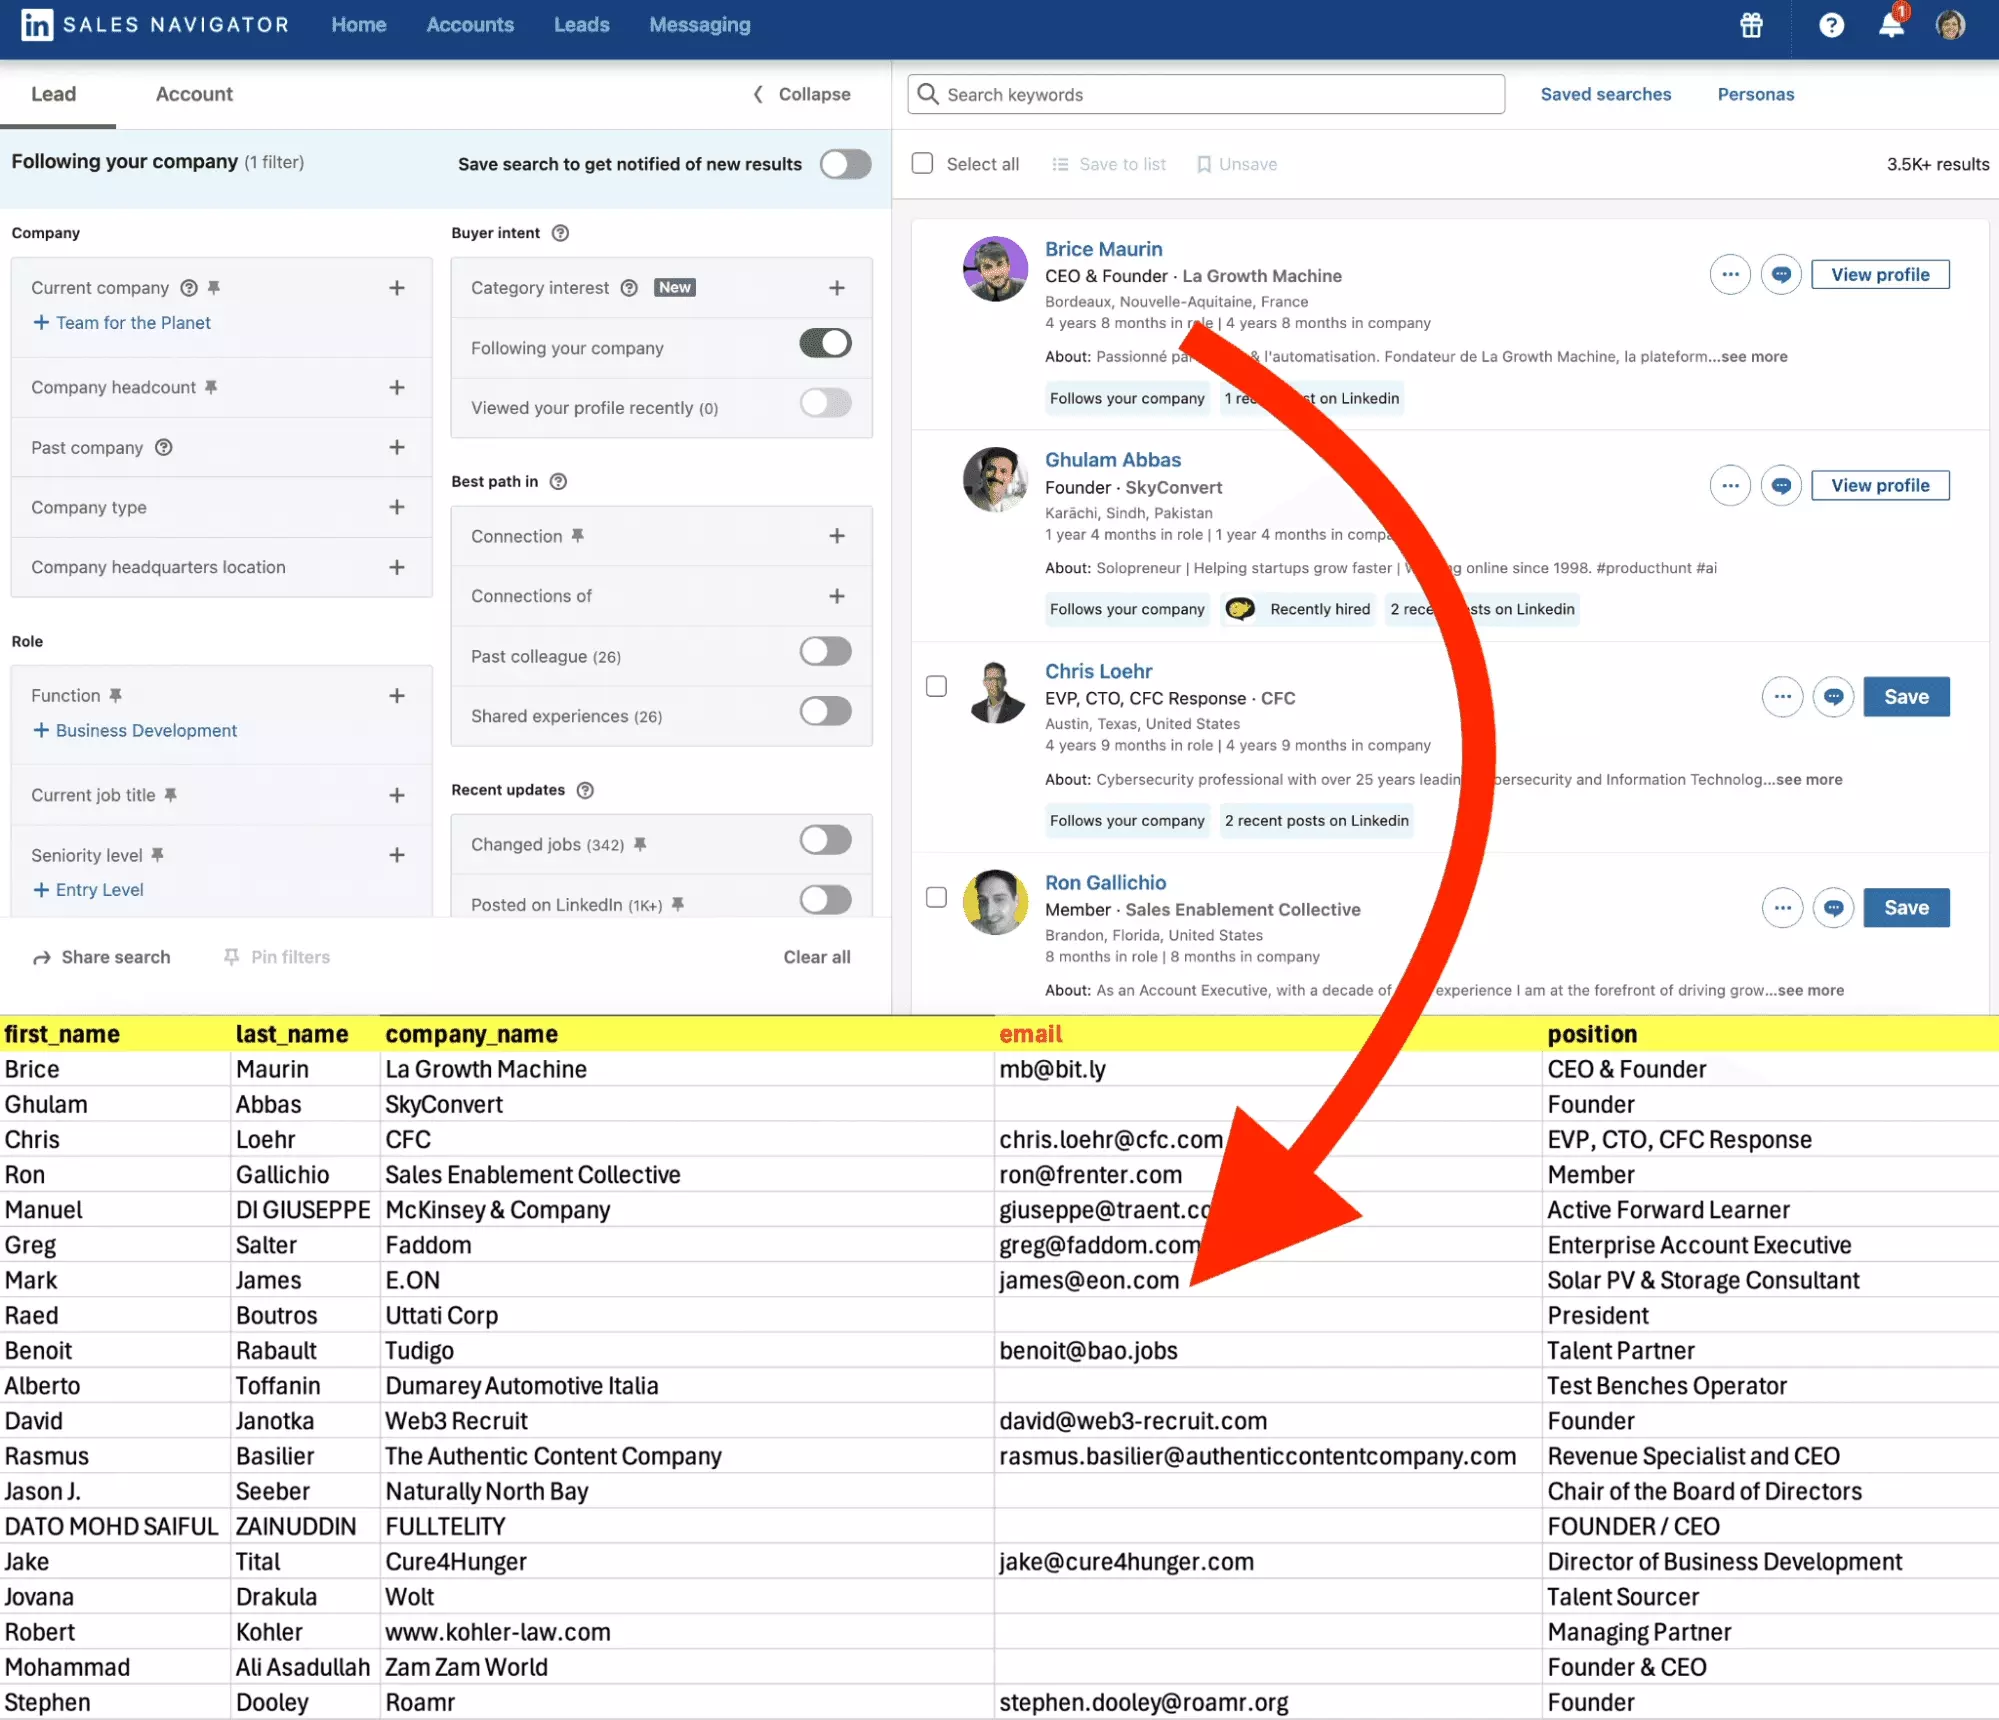
Sales Navigator search results exported to a spreadsheet with emails

Bullet 2 still does. Exporting with a tool is against LinkedIn's terms, and the risk is the same as anywhere on the platform: your account.

LinkedIn caps every Sales Navigator search at 2,500 results and watches how fast you page through them.

Your subscription buys you the view, not a licence to hammer it.
And GDPR applies to your export exactly like a public profile. The full process is in how to scrape LinkedIn Sales Navigator, the tool comparison in the best Sales Navigator leads scrapers.

So how do you scrape LinkedIn at scale without ending up like those four companies?

How to scrape LinkedIn at scale, legally

Every lawsuit and the one fine above come down to four things: your own account, only what you can legitimately see, no database to resell, and limits respected.

That's how lobstr.io is built, so let me use it as the example.
Your account, your cookies, never your password. You connect LinkedIn or Sales Navigator through the Account Sync extension, which only captures your session cookies.

We never ask for credentials, and we never use fake or bought accounts.
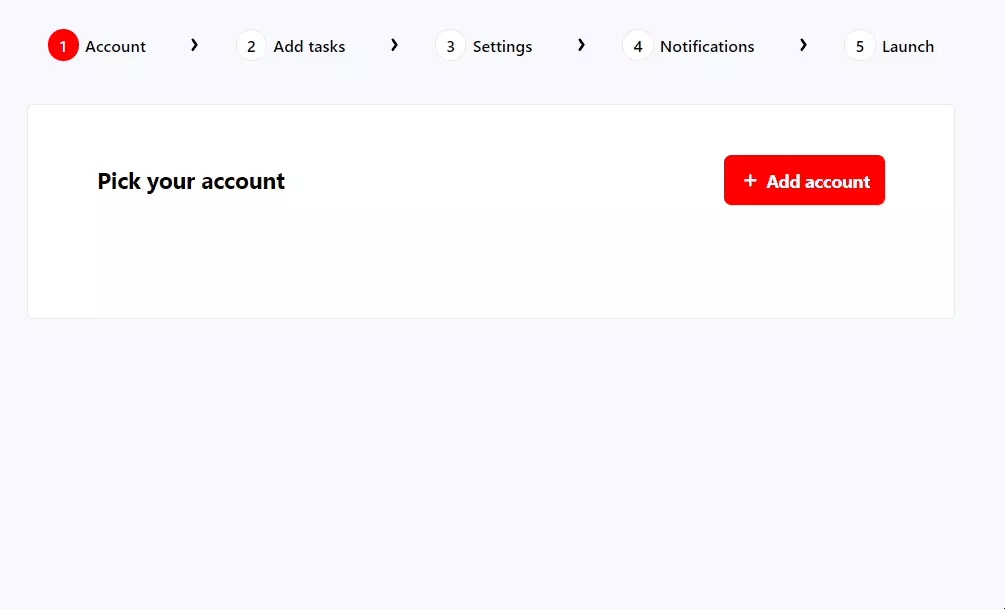
lobstr.io Squid setup: pick your synced account

The scraper then does what you'd do in your browser, on your own seat, just faster.
Limits you can't blow through by accident. Every synced account is capped at 5,000 Sales Navigator leads and 200 searches a day. If LinkedIn throws a rate limit, the run pauses on its own instead of pushing through.
No database, no resale. Your results stay downloadable for 30 days, then they're deleted. Under our personal data agreement you're the controller and we're your processor, and your account data goes within six months of termination. No LinkedIn database, nothing to sell.
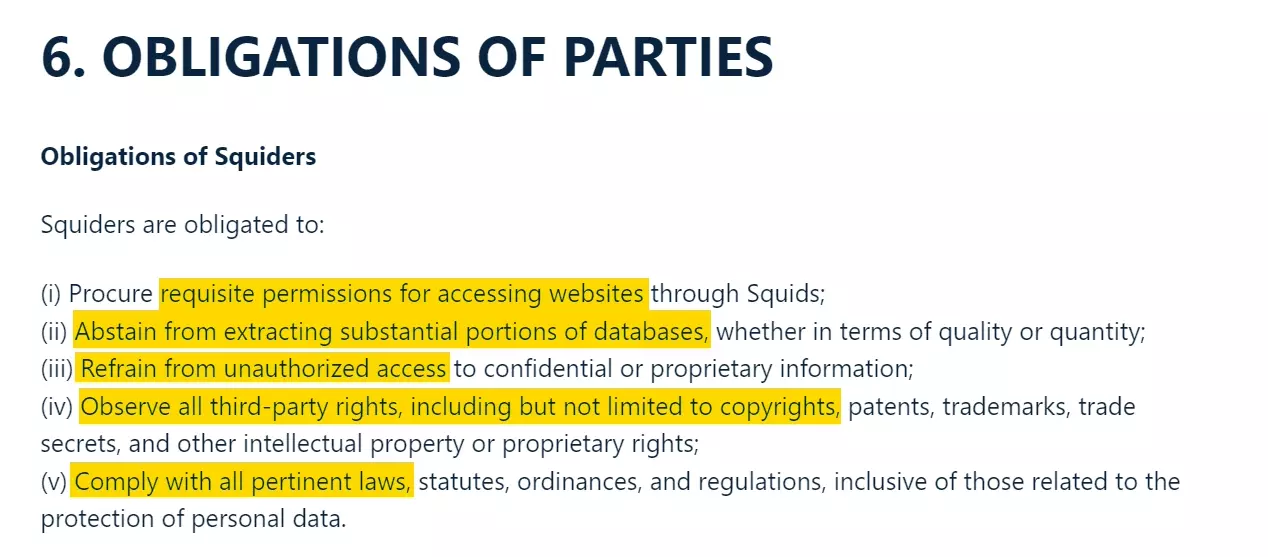
The rules are in writing. Our terms of use ask every user for legitimate access, no substantial extraction from a database, and respect for personal data law.
lobstr.io terms of use, section 6, obligations of Squiders
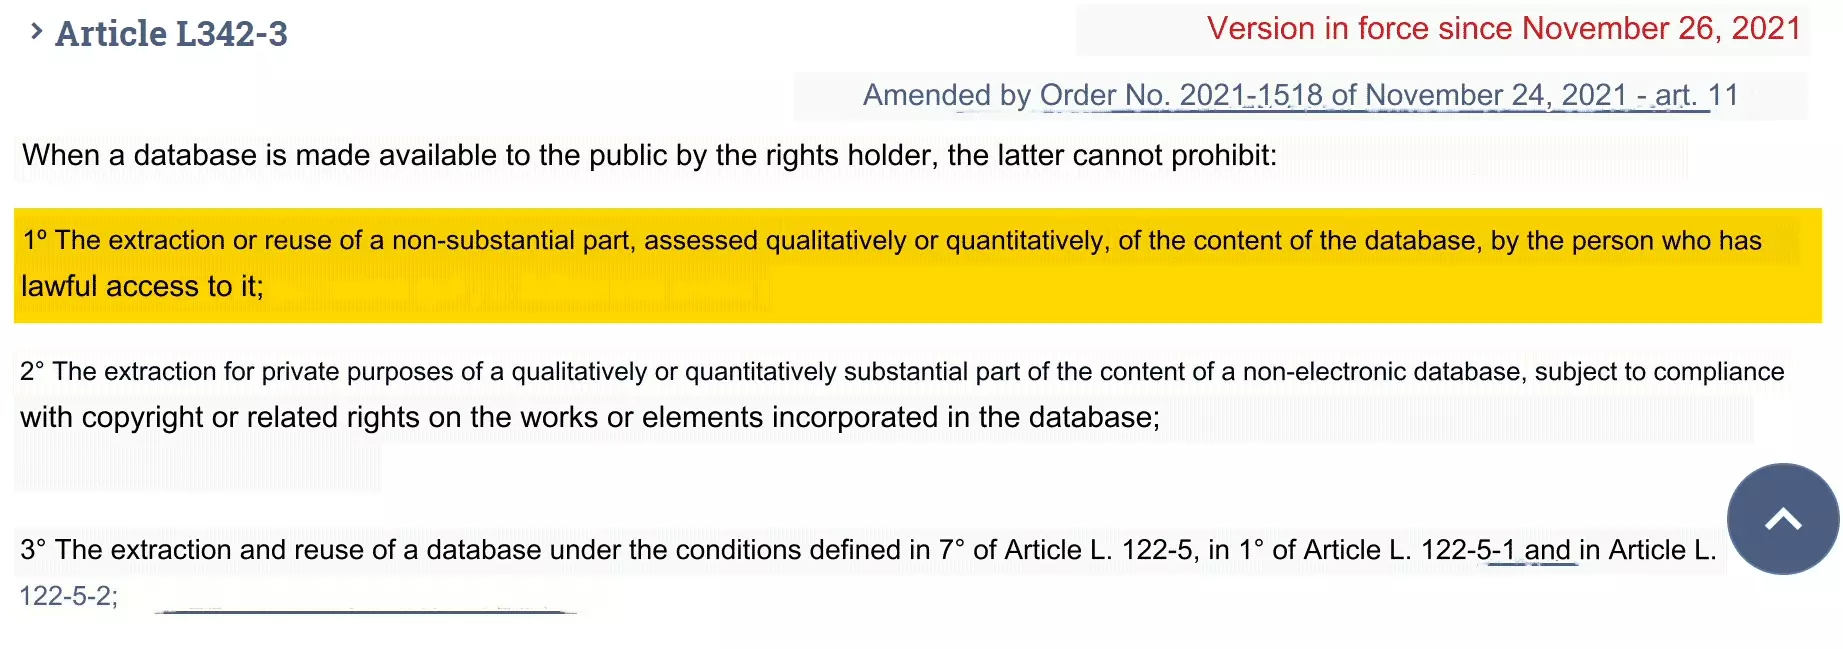
That middle rule is French law. Article L342-3 of the intellectual property code lets anyone with lawful access extract non-substantial parts of a public database, and L342-2 forbids doing it repeatedly. We're based in France, so we live under both.
LΓ©gifrance, Article L342-3 of the French intellectual property code
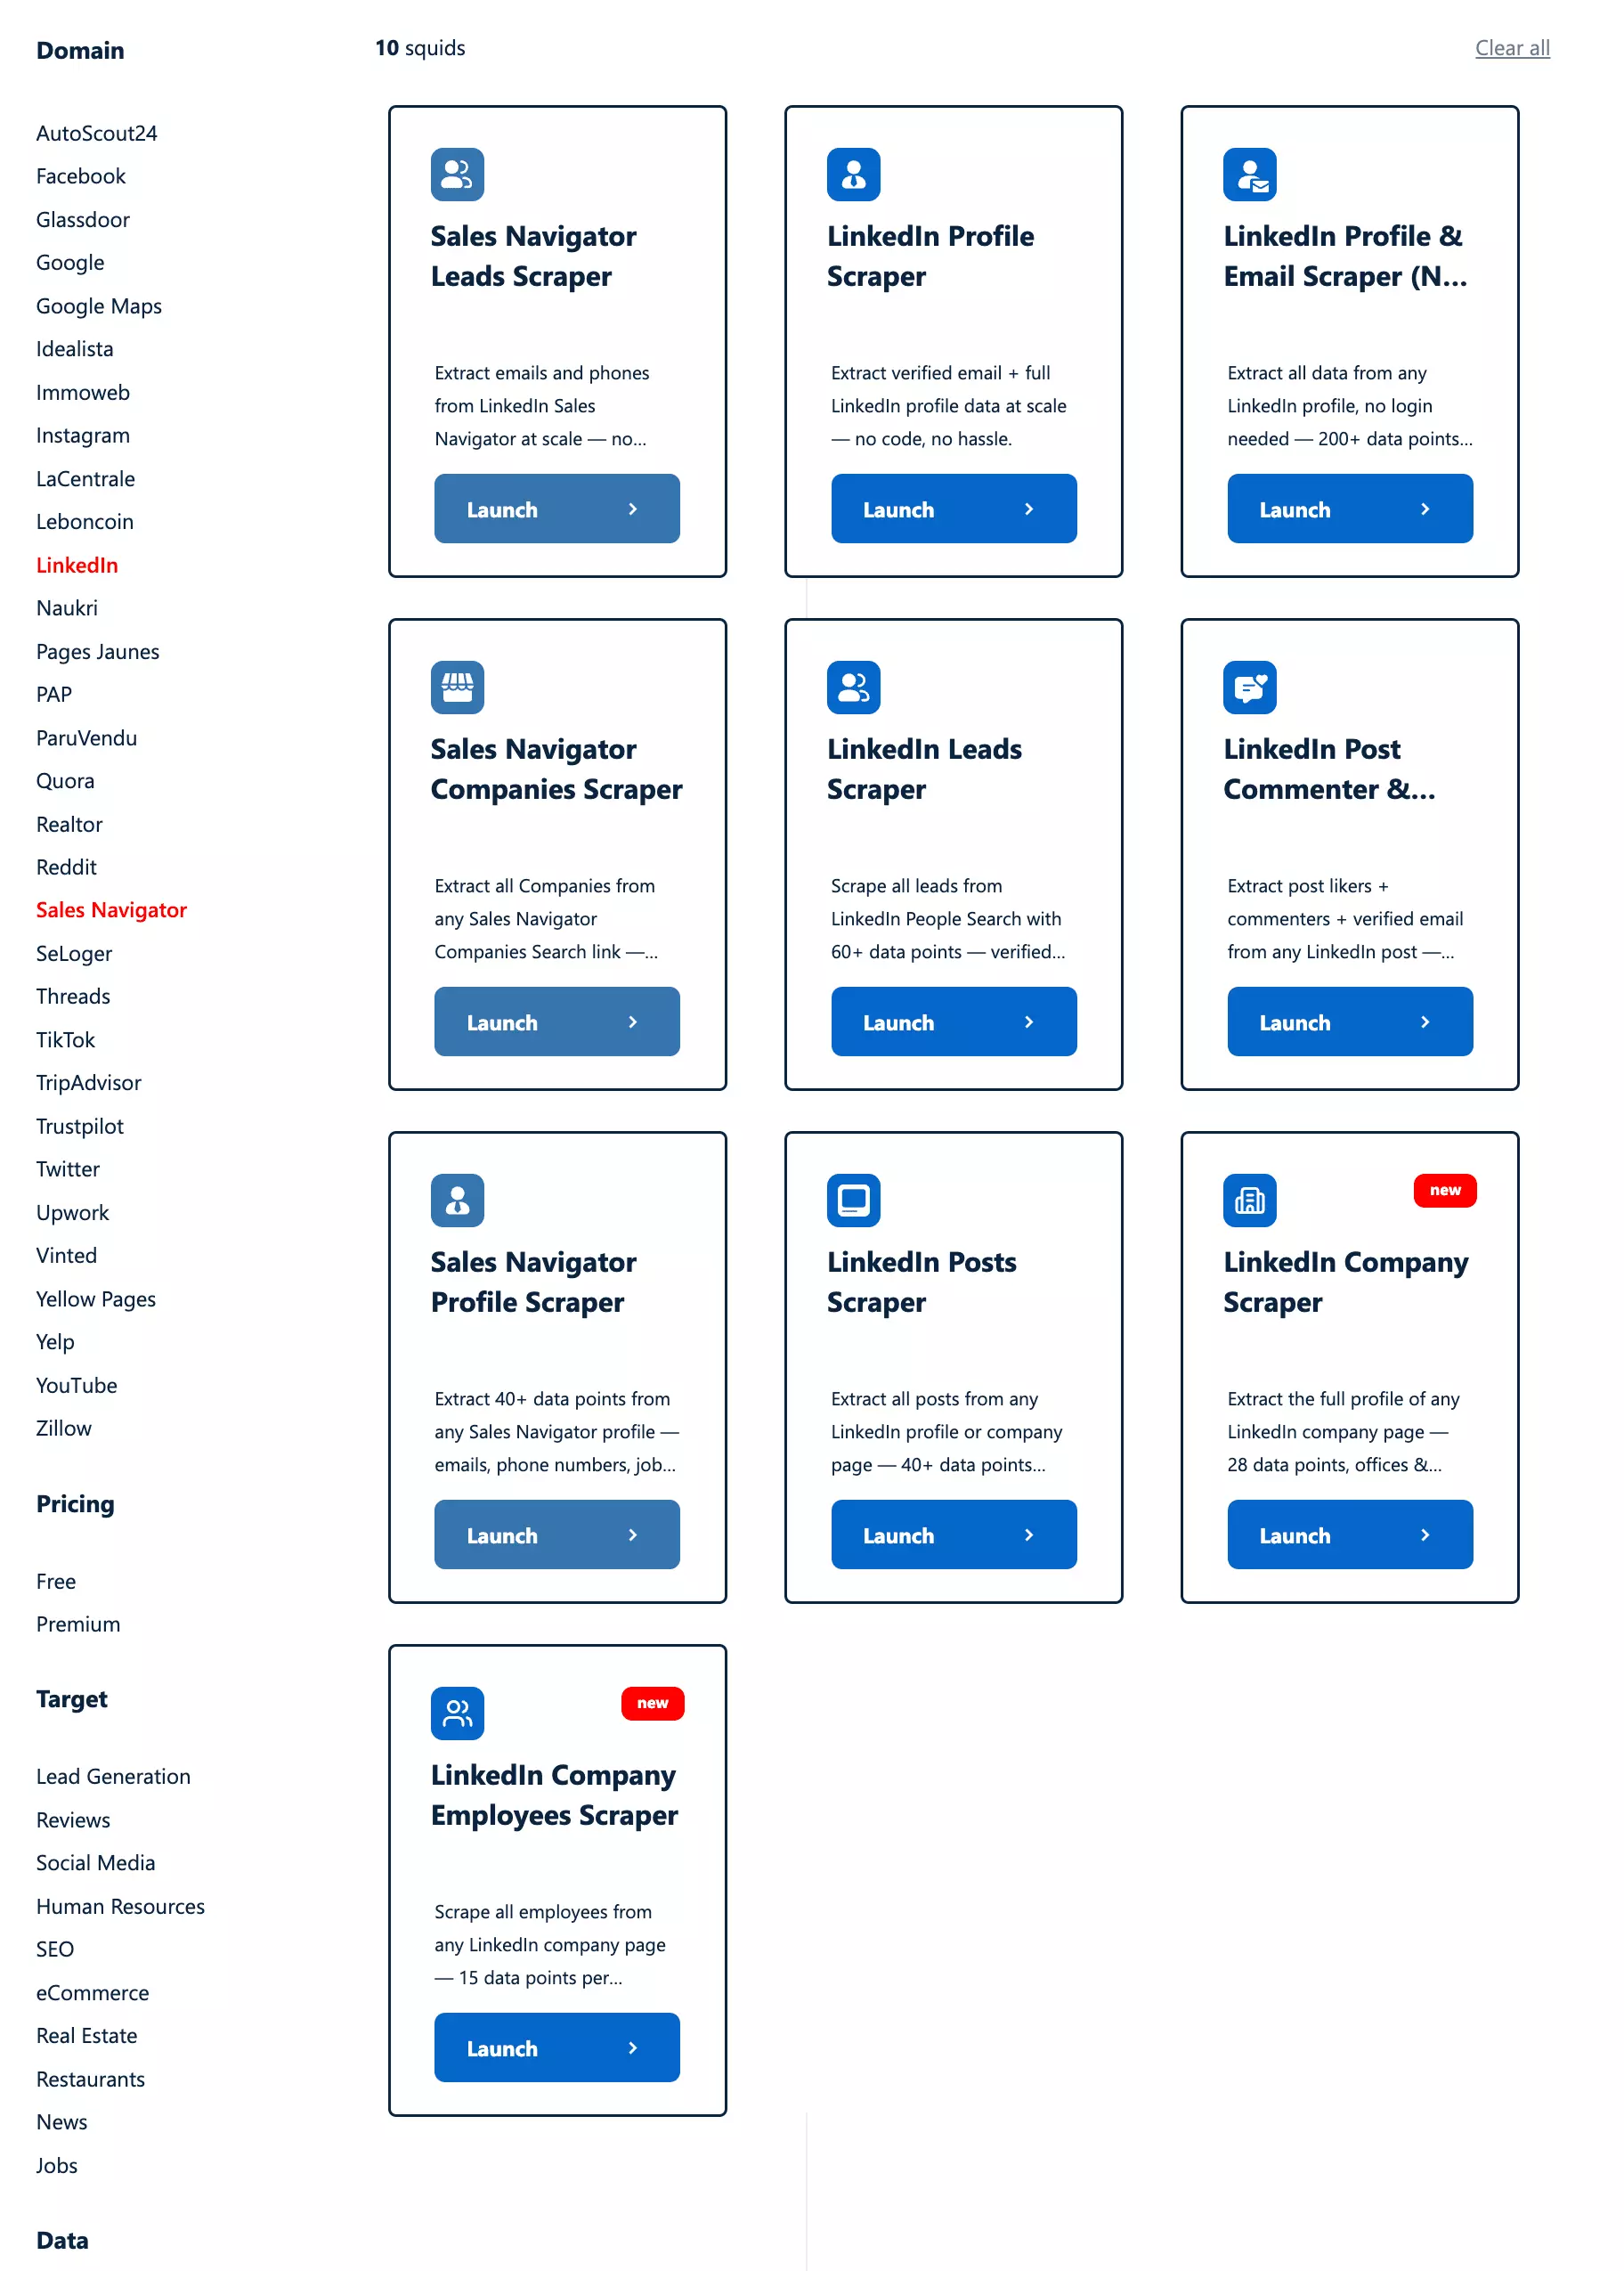
Every LinkedIn scraper we offer works the same way: profiles, leads from LinkedIn search, posts, post commenters and likers, companies and their employees, plus Sales Navigator leads, companies and profiles. Not sure which one you need? Start with the best LinkedIn profile scrapers πŸ‘€
How to scrape LinkedIn at scale, legally
Prefer the terminal? The CLI runs every scraper on the same synced account:
pip install lobstrio export LOBSTR_TOKEN=your_api_key lobstr go sales-navigator-leads-scraper "https://linkedin.com/..." --account jane@example.com
f
And if you live in Claude or ChatGPT, plug your agent in through the MCP server. You log in on lobstr.io, so your password never reaches the AI either:
claude mcp add --transport http lobstr https://mcp.lobstr.io/mcp
f

Got more questions? So did our readers πŸ‘‡

FAQ

Is LinkedIn scraping illegal?

No, it's not a crime in the US, France or the EU, based on every case above. It does break LinkedIn's User Agreement, a contract, and any personal data you collect falls under GDPR.

Does LinkedIn allow data scraping?

No, section 8.2 of the User Agreement bans it, effective 3 November 2025. If you get caught, your account gets restricted until you stop using the tool.

Will LinkedIn ban me for scraping?

It can restrict your account, and it spots automation by behaviour, not a fixed number. That's why lobstr.io caps every synced account at 5,000 Sales Navigator leads and 200 searches a day.

Did hiQ win against LinkedIn?

No, hiQ lost on breach of contract in November 2022 and paid $500,000 a month later. The famous April 2022 ruling only said scraping public pages isn't hacking under the CFAA.

Not a crime on your own paid seat. You're exporting what LinkedIn already shows you. Fake or bought accounts are what got Mantheos, Proxycurl and ProAPIs sued.

Does GDPR apply if the profile is public?

Yes, public data is still personal data. The CNIL fined Kaspr €240,000 for scraping LinkedIn contacts, partly for taking details people had hidden. Legitimate interest works if you inform people and honour opt-outs.

Is buying a scraped LinkedIn list different from scraping it?

It's riskier, not safer. You inherit data with no legal basis, nobody was told about it, and you have no idea whether fake accounts collected it.

Is using an AI agent to scrape LinkedIn a loophole?

No, the same rules apply. An agent calling a scraper through MCP runs on the same account, under the same terms and the same GDPR duties.

Final thoughts

Scraping LinkedIn is not a crime, and nothing in 2026 changed that. What the lawsuits and the Kaspr fine did change is who we know gets in trouble: people running fake accounts, reselling paywalled data, and hoarding personal data without telling anyone.

Stay on your own account, export what you can already see, keep only what you need, and give people a way out. Nobody who did that has ever been sued.

I'll update this page when the ProAPIs case closes and the EDPB finalises its guidelines. Spotted a ruling I missed? Ping me on LinkedIn 🦞

Related Articles

Related Squids